Microsoft 365 Security Best Practices for Healthcare Organizations
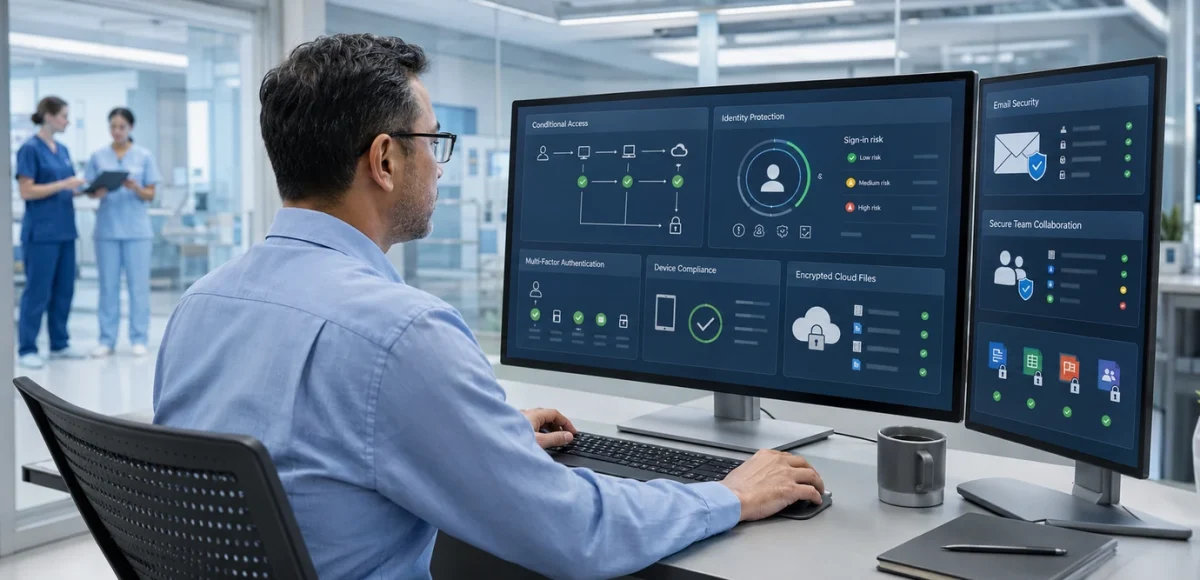
Microsoft 365 has become the productivity platform of choice for many healthcare organizations, supporting email, collaboration, document management, video conferencing, and cloud storage. While Microsoft provides a highly secure cloud platform, protecting your organization’s Microsoft 365 environment remains a shared responsibility. Every healthcare organization should implement strong identity management, Multi-Factor Authentication (MFA), Conditional Access, data protection, email security, endpoint protection, and user awareness training to reduce cybersecurity risks and protect patient information.
Who This Guide Is For
This guide is designed for:
- Physicians
- Medical Practice Owners
- Dental Practice Owners
- Practice Administrators
- Healthcare Executives
- Office Managers
- Compliance Officers
- IT Managers
- Behavioral Health Providers
- Home Health Organizations
Whether your organization has recently migrated to Microsoft 365 or has been using it for years, this guide will help you understand how to strengthen security while supporting productivity, collaboration, and patient care.
Why Microsoft 365 Has Become Essential in Healthcare
Healthcare has become increasingly mobile, collaborative, and cloud-connected.
Providers communicate through email.
Practice managers collaborate using Microsoft Teams.
Documents are stored in SharePoint and OneDrive.
Employees access information from multiple locations and devices.
These capabilities improve efficiency and support better patient care but they also expand the organization’s cybersecurity responsibilities.
A compromised Microsoft 365 account may provide attackers access to:
- Email communications
- Shared documents
- Microsoft Teams conversations
- Patient-related administrative information
- Financial records
- Human Resources files
- Organizational calendars
- Internal policies and procedures
Because Microsoft 365 often serves as the central hub for business operations, protecting it should be one of every healthcare organization’s highest cybersecurity priorities.
Why This Matters to Your Practice
For many healthcare organizations, Microsoft 365 is more than an email platform. It has become the operational center for communication, collaboration, document management, and business productivity. Protecting Microsoft 365 helps protect the daily operations that support patient care.
Microsoft 365 Security Is a Shared Responsibility
One of the biggest misconceptions about cloud computing is:
“Our data is in Microsoft 365, so Microsoft secures everything.”
This isn’t entirely accurate.
Microsoft is responsible for securing the underlying cloud infrastructure that delivers Microsoft 365 services.
Healthcare organizations remain responsible for how their own Microsoft 365 environment is configured, managed, and used.
This is commonly referred to as the Shared Responsibility Model.
Microsoft helps protect:
- Global cloud infrastructure
- Physical datacenters
- Platform availability
- Core service security
- Infrastructure resilience
Healthcare organizations remain responsible for:
- User accounts
- Password policies
- Multi-Factor Authentication
- Access permissions
- Device security
- Data governance
- Information sharing
- User awareness
- Security monitoring
- Organizational policies
Cloud services reduce some infrastructure responsibilities but they do not eliminate cybersecurity responsibilities.
Expert Tip
Moving to Microsoft 365 can improve flexibility and resilience, but cloud adoption should never be viewed as a replacement for cybersecurity governance. Secure configurations, workforce education, and ongoing monitoring remain essential.
Why Healthcare Organizations Are Frequently Targeted
Healthcare organizations rely heavily on email and cloud collaboration.
Cybercriminals know this.
Compromising one Microsoft 365 account may allow attackers to:
- Read email
- Send phishing messages internally
- Access shared files
- Collect employee information
- Target financial personnel
- Launch Business Email Compromise (BEC) attacks
- Expand access to additional systems
Because many organizations also use Microsoft 365 credentials to access other business applications through Single Sign-On (SSO), one compromised account can have organization-wide consequences.
The Most Important Microsoft 365 Security Controls
While Microsoft provides hundreds of security capabilities, healthcare organizations should focus first on implementing foundational controls that reduce the greatest risks.
1. Multi-Factor Authentication (MFA)
If there is one security improvement nearly every healthcare organization should prioritize, it is Multi-Factor Authentication.
MFA requires users to verify their identity using more than just a password.
Examples include:
- Microsoft Authenticator
- Authentication apps
- Hardware security keys
- Passkeys
- Biometric verification
Even if an attacker steals a password, MFA significantly reduces the likelihood that the account can be accessed.
Healthcare organizations should prioritize MFA for:
- Global administrators
- Executives
- Physicians
- Financial personnel
- Remote users
- Microsoft 365 administrators
- All employee accounts whenever practical
MFA remains one of the highest-impact security improvements available.
2. Conditional Access
Not every login attempt should be treated equally.
Conditional Access allows organizations to establish rules based on risk.
Examples include:
- Requiring MFA outside trusted locations
- Blocking sign-ins from unexpected countries
- Restricting legacy authentication
- Requiring compliant devices
- Limiting administrative access
- Responding to elevated sign-in risk
Conditional Access helps organizations balance security with user convenience by adapting authentication requirements based on context.
3. Identity Protection
Compromised identities remain one of the leading causes of successful cyberattacks.
Identity protection focuses on detecting unusual account behavior before it leads to larger security incidents.
Organizations should monitor for:
- Impossible travel
- Repeated failed sign-ins
- Unusual login locations
- Anonymous IP usage
- Suspicious authentication attempts
- Privilege escalation
Rapid identification of suspicious identity activity allows organizations to respond before attackers establish long-term access.
4. Secure Email
Email continues to be the most common entry point for cyberattacks.
Healthcare organizations should strengthen email security through layered protections that include:
- Anti-phishing protections
- Spam filtering
- Safe attachment scanning
- Safe link protection
- Email authentication
- User awareness training
Technology helps filter malicious messages.
Employees remain the final layer of defense.
5. Secure Microsoft Teams Collaboration
Microsoft Teams has become a primary communication platform for many healthcare organizations.
Clinical teams collaborate.
Practice administrators coordinate schedules.
Leadership conducts meetings.
Documents are shared.
External vendors participate in conversations.
While Teams improves communication and productivity, it should also be governed with appropriate security controls.
Healthcare organizations should establish policies that address:
- Who can create Teams
- Guest access permissions
- External collaboration
- File sharing
- Meeting security
- Screen sharing
- Chat retention
- Recording permissions
- Mobile device access
Without governance, Teams environments can quickly become difficult to manage and increase the risk of unintended information sharing.
Why This Matters to Your Practice
Collaboration tools make it easier for employees to work together, but they can also make it easier to accidentally overshare sensitive information. Clear governance helps balance productivity with security.
6. Protect SharePoint and OneDrive Data
Microsoft 365 stores a tremendous amount of organizational knowledge.
Policies.
Financial records.
Human Resources documents.
Operational procedures.
Marketing materials.
Contracts.
Business records.
In some healthcare organizations, documents containing sensitive information may also be stored within SharePoint or OneDrive.
Organizations should establish governance around:
- File permissions
- External sharing
- Data ownership
- Version control
- Retention policies
- Secure document storage
- Periodic permission reviews
One of the most common security mistakes is granting “Everyone” access to folders that should only be available to specific departments.
Access should be reviewed periodically as employees change roles or leave the organization.
7. Implement Data Loss Prevention (DLP)
Data Loss Prevention (DLP) helps reduce the risk of sensitive information being shared inappropriately.
Depending on licensing and organizational requirements, DLP policies can help identify and respond to attempts to share information such as:
- Social Security numbers
- Financial account information
- Employee records
- Other sensitive organizational data
Healthcare organizations should thoughtfully evaluate where DLP policies can improve governance while minimizing unnecessary workflow disruptions.
DLP is most effective when combined with employee education and clearly documented information handling policies.
8. Strengthen Administrative Security
Administrative accounts represent one of the highest-value targets for attackers.
A compromised administrator account may provide broad access across the Microsoft 365 environment.
Organizations should consider implementing:
- Separate administrator accounts
- Dedicated administrative workstations where appropriate
- Privileged Access Management (PAM) where available
- Just-in-time administrative access
- Regular administrative account reviews
- Administrative activity logging
Administrative privileges should only be granted to individuals who require them to perform their responsibilities.
Expert Tip
Employees should use separate accounts for everyday work and administrative tasks whenever practical. Reducing daily use of privileged accounts helps limit exposure if credentials are compromised.
9. Secure Mobile Devices
Healthcare professionals increasingly access Microsoft 365 using:
- Smartphones
- Tablets
- Laptops
- Personally owned devices
- Shared clinical workstations
This flexibility improves patient care and operational efficiency but also expands the organization’s attack surface.
Organizations should establish policies addressing:
- Device encryption
- Screen lock requirements
- Remote wipe capabilities
- Approved mobile applications
- Lost device reporting
- Bring Your Own Device (BYOD) expectations
Secure mobile access supports workforce flexibility while helping protect organizational data.
10. Monitor Sign-In Activity
Security monitoring should not begin after an incident.
Healthcare organizations should regularly review Microsoft 365 sign-in activity for indicators of unusual behavior.
Examples include:
- Impossible travel
- Logins from unfamiliar countries
- Multiple failed sign-in attempts
- Authentication from anonymous networks
- Privileged account activity
- Unusual login times
- Disabled security controls
Early detection often allows organizations to respond before suspicious activity develops into a larger security incident.
Common Microsoft 365 Security Mistakes Healthcare Organizations Should Avoid
Technology alone cannot compensate for poor security practices.
The following mistakes appear frequently across healthcare organizations of all sizes.
Mistake #1: Assuming Microsoft Secures Everything
Microsoft secures the cloud platform.
Your organization secures its users, identities, configurations, permissions, and data.
Understanding the Shared Responsibility Model is one of the most important steps toward improving Microsoft 365 security.
Mistake #2: Not Enabling MFA for Every User
Some organizations only require Multi-Factor Authentication for administrators.
Attackers, however, often compromise standard user accounts first.
Whenever practical, MFA should be enabled across the organization.
Mistake #3: Excessive Permissions
Employees sometimes retain access long after changing roles.
Over time this creates unnecessary risk.
Organizations should periodically review:
- User permissions
- Group memberships
- Shared mailbox access
- SharePoint permissions
- Teams ownership
- Administrative privileges
Access should align with current job responsibilities.
Mistake #4: Uncontrolled External Sharing
Cloud collaboration makes sharing easy.
Sometimes too easy.
Organizations should establish policies governing:
- Guest access
- External file sharing
- Anonymous links
- Vendor collaboration
- Expiration dates for shared content
Not every document should be accessible outside the organization.
Mistake #5: Ignoring Security Alerts
Microsoft 365 generates valuable security information.
Alerts should be reviewed regularly rather than dismissed or ignored.
Responding promptly to suspicious activity may prevent more serious incidents.
Mistake #6: Lack of Employee Training
Even the best security technologies cannot eliminate human error.
Employees should understand:
- Phishing attacks
- Business Email Compromise (BEC)
- Credential theft
- AI-assisted scams
- Safe file sharing
- Password hygiene
- Reporting suspicious activity
Education strengthens every other security investment.
Why This Matters to Your Practice
Most successful Microsoft 365 compromises result from a combination of small issues and not just from a single catastrophic failure. Addressing common configuration gaps, strengthening identity security, and educating employees significantly reduces organizational risk.
Building a Secure Microsoft 365 Environment
Strong Microsoft 365 security isn’t achieved through a single setting.
It results from layered protections working together.
These layers include:
- Identity protection
- Multi-Factor Authentication
- Conditional Access
- Endpoint security
- Email protection
- Data governance
- Device management
- Administrative controls
- Security monitoring
- Workforce education
Organizations that treat Microsoft 365 as a strategic business platform rather than simply an email service are generally better positioned to support secure, reliable healthcare operations.
Microsoft 365 Security Self-Assessment Checklist
Microsoft 365 security is not defined by a single configuration or security feature.
Instead, it reflects how well your organization protects identities, secures data, manages devices, governs collaboration, and prepares for evolving cyber threats.
Use this checklist to evaluate your current Microsoft 365 environment.
This assessment is intended to help healthcare leaders identify strengths, uncover opportunities for improvement, and prioritize future security initiatives. It complements but does not replace a formal Security Risk Assessment or Microsoft 365 security review.
Identity & Authentication
- Multi-Factor Authentication (MFA) is enabled for all users whenever practical.
- Administrative accounts require stronger authentication controls.
- Password policies align with current security best practices.
- Legacy authentication has been disabled where possible.
- User sign-in activity is monitored.
- High-risk sign-in events are investigated promptly.
Strong identity protection forms the foundation of Microsoft 365 security.
Conditional Access
- Conditional Access policies have been implemented.
- Administrative accounts have additional protections.
- Access from unexpected geographic locations is restricted when appropriate.
- Risk-based authentication policies are in place.
- Access from unmanaged devices is evaluated.
- Policies are reviewed periodically as organizational needs evolve.
Conditional Access helps organizations balance productivity with security by adapting protections based on user behavior and risk.
Administrative Security
- Administrative accounts are separate from standard user accounts.
- Administrative privileges are reviewed regularly.
- Only authorized personnel have elevated permissions.
- Administrative activity is monitored.
- Emergency access procedures are documented.
- Administrative accounts are protected with the highest level of security available.
Limiting privileged access significantly reduces organizational risk.
Why This Matters to Your Practice
Administrative accounts can control nearly every aspect of your Microsoft 365 environment. Protecting these accounts helps safeguard email, collaboration tools, documents, user identities, and business operations.
Email Security
- Anti-phishing protections are enabled.
- Spam filtering is configured appropriately.
- Safe attachment protections are active.
- Safe link protections are implemented.
- Email authentication technologies are configured.
- Employees receive phishing awareness training.
Email remains one of the most common attack vectors targeting healthcare organizations.
Microsoft Teams Governance
- Guest access policies have been established.
- External collaboration settings are reviewed.
- Team creation is governed appropriately.
- Meeting security settings have been evaluated.
- Recording permissions align with organizational policies.
- Teams ownership is reviewed periodically.
Effective governance helps organizations collaborate securely without creating unnecessary operational risk.
SharePoint & OneDrive Security
- External sharing policies are documented.
- File permissions are reviewed regularly.
- Sensitive information is stored appropriately.
- Departmental access aligns with business responsibilities.
- Data retention policies have been established.
- Version history is enabled where appropriate.
Organizations should periodically review permissions to ensure employees have access only to the information required for their current responsibilities.
Endpoint & Device Security
- Organization-owned devices are managed appropriately.
- Mobile devices follow organizational security policies.
- Device encryption has been enabled where appropriate.
- Lost or stolen devices can be remotely managed.
- Endpoint Detection and Response (EDR) protects supported devices.
- Device compliance is reviewed regularly.
Secure identities become significantly more effective when paired with secure endpoints.
Data Protection
- Sensitive organizational information has been identified.
- Data Loss Prevention (DLP) policies have been evaluated.
- External sharing aligns with organizational policies.
- Information governance procedures are documented.
- Backup strategies have been reviewed.
- Critical business information is protected appropriately.
Data protection extends beyond preventing cyberattacks. It also helps ensure that information is available, accurate, and appropriately governed throughout its lifecycle.
Security Monitoring
- Security alerts are reviewed regularly.
- Sign-in logs are monitored.
- Suspicious account activity is investigated.
- Administrative changes are documented.
- Incident Response procedures include Microsoft 365.
- Security monitoring responsibilities are clearly assigned.
Continuous visibility allows organizations to detect suspicious behavior before it develops into a larger incident.
Workforce Awareness
- Employees understand phishing attacks.
- Staff recognize Business Email Compromise (BEC).
- Employees understand safe file-sharing practices.
- AI-assisted phishing risks are discussed during training.
- Employees know how to report suspicious emails.
- Security awareness is reinforced throughout the year.
Technology provides important protections but informed employees remain one of the strongest cybersecurity defenses.
Expert Tip
Microsoft 365 security improves most when organizations regularly review identities, permissions, collaboration settings, and employee awareness rather than only after implementing new technology.
Understanding Your Microsoft 365 Security Maturity
After completing the checklist, consider where your organization falls within the following maturity framework.
Emerging
Your organization has adopted Microsoft 365 but still relies primarily on default configurations.
Common opportunities include:
- Expanding MFA adoption
- Improving identity management
- Establishing collaboration governance
- Strengthening endpoint security
- Developing formal Microsoft 365 policies
Organizations at this stage often benefit most from building consistent governance before implementing more advanced security capabilities.
Developing
Foundational Microsoft 365 security controls have been implemented.
Characteristics often include:
- Organization-wide MFA
- Conditional Access
- Email security improvements
- Endpoint protection
- Basic governance
- Security awareness training
The next phase focuses on improving visibility, consistency, and continuous security management.
Mature
Microsoft 365 security has become part of a broader organizational cybersecurity strategy.
Characteristics often include:
- Risk-based Conditional Access
- Strong administrative governance
- Advanced identity protection
- Structured information governance
- Ongoing security monitoring
- Executive oversight
- Incident Response integration
- Continuous workforce education
Mature organizations recognize that Microsoft 365 security evolves alongside organizational growth, cloud adoption, and emerging cyber threats.
Why This Matters to Your Practice
The objective isn’t to enable every Microsoft security feature. It’s to implement the controls that best support your organization’s operational needs, risk profile, regulatory responsibilities, and long-term technology strategy.
Measuring Microsoft 365 Security Success
Healthcare leaders often ask:
“How do we know if our Microsoft 365 environment is becoming more secure?”
Meaningful indicators may include:
- Multi-Factor Authentication adoption approaches 100%.
- Administrative accounts are tightly controlled.
- Fewer employees fall for phishing simulations.
- Security alerts are reviewed and resolved promptly.
- External sharing is governed consistently.
- Access permissions remain current.
- Device compliance improves over time.
- Incident Response procedures are tested.
- Leadership receives regular security reporting.
- Employees demonstrate greater cybersecurity awareness.
Effective security programs measure operational improvement, not simply the number of features enabled.
Microsoft 365 Security Is an Ongoing Process
Cloud platforms continue to evolve.
Cyber threats continue to evolve.
Healthcare workflows continue to evolve.
Artificial Intelligence continues to evolve.
Maintaining a secure Microsoft 365 environment requires ongoing governance, regular reviews, employee education, and continuous improvement.
Organizations that periodically evaluate their Microsoft 365 environment are generally better positioned to protect sensitive information, reduce operational risk, and support reliable patient care.
Executive Summary for Healthcare Leaders
If you remember only five things from this guide, make them these:
1. Microsoft 365 Is a Business Platform, Not Just Email
For many healthcare organizations, Microsoft 365 supports communication, collaboration, document management, scheduling, and day-to-day operations.
Protecting the platform helps protect the business functions that support patient care.
2. Security Is a Shared Responsibility
Microsoft secures the cloud infrastructure.
Your organization secures identities, users, permissions, devices, information, and governance.
Understanding this distinction is essential to reducing cyber risk.
3. Identity Protection Should Be Your First Priority
Strong passwords alone are no longer enough.
Multi-Factor Authentication, Conditional Access, identity monitoring, and privileged access management form the foundation of Microsoft 365 security.
4. Collaboration Requires Governance
Microsoft Teams, SharePoint, and OneDrive make collaboration easier, but they also require thoughtful governance around permissions, external sharing, retention, and information management.
Good governance enables productivity while reducing unnecessary risk.
5. Continuous Improvement Builds Resilience
Microsoft 365 security isn’t a one-time project.
Organizations that review configurations, educate employees, monitor security events, and refine governance over time are better positioned to adapt to changing technologies and emerging cyber threats.
How Fothion Helps Healthcare Organizations Secure Microsoft 365
Microsoft 365 is one of the most important technology platforms within modern healthcare organizations.
Securing it requires more than enabling a few settings.
It requires planning, governance, ongoing monitoring, and a clear understanding of how technology supports patient care.
Fothion helps healthcare organizations strengthen Microsoft 365 through services that include:
- Microsoft 365 security assessments
- Identity and access management
- Multi-Factor Authentication (MFA) deployment
- Conditional Access planning
- Microsoft Teams governance
- SharePoint and OneDrive security guidance
- Endpoint Detection and Response (EDR)
- Microsoft Intune device management
- Security awareness training
- Backup and Business Continuity planning
- Strategic IT consulting
- Ongoing managed IT support
Our objective is to help healthcare organizations maximize the value of Microsoft 365 while reducing cybersecurity risk and supporting secure, efficient clinical and business operations.
Schedule a Microsoft 365 Security Assessment
If your organization has never completed a structured Microsoft 365 security review, or if it has been several years since your last assessment, it may be time to evaluate your environment.
A Microsoft 365 Security Assessment can help your organization:
- Review identity security
- Evaluate Multi-Factor Authentication adoption
- Assess Conditional Access policies
- Strengthen collaboration governance
- Improve data protection
- Identify configuration gaps
- Reduce cybersecurity risk
- Support long-term technology planning
A proactive assessment helps leadership make informed decisions about security investments before small issues become larger operational risks.
Book your 30-minute call with Fothion now:

Continue Learning About Healthcare IT & Cybersecurity
Continue building your healthcare technology knowledge with these related guides:
- HIPAA Compliance for Medical Practices: What Every Healthcare Organization Needs to Know
- Healthcare Cybersecurity Checklist: Essential Security Controls Every Medical Practice Should Have
- Ransomware Attacks on Medical Practices: What Happens, How to Respond, and How to Protect Your Patients
- How to Create Secure Technology Policies for Your Medical or Dental Practice
- Can Healthcare Professionals Use AI Tools Like ChatGPT Without Violating HIPAA?
- How to Choose the Right IT Provider for Your Medical or Dental Practice
Together, these Industry Insights provide healthcare leaders with practical guidance for strengthening cybersecurity, improving governance, and making informed technology decisions.
About This Guide
This article is part of Fothion’s Industry Insights which is a growing collection of educational resources created specifically for healthcare organizations navigating today’s rapidly evolving technology landscape.
Rather than focusing solely on software features, our Healthcare IT insights explain how technology decisions affect cybersecurity, compliance, operational resilience, workforce productivity, and patient care.
Our mission is to help physicians, administrators, executives, and healthcare leaders make informed technology decisions with confidence through practical, vendor-neutral education grounded in real-world healthcare operations.
Educational Disclaimer
This article is provided for educational and informational purposes only and should not be interpreted as legal, regulatory, compliance, cybersecurity, or technical implementation advice. Every healthcare organization has unique operational, contractual, security, and regulatory requirements that should be evaluated individually.
Healthcare organizations should consult qualified legal counsel, compliance professionals, cybersecurity specialists, and experienced technology advisors when designing Microsoft 365 security strategies, configuring security controls, implementing governance policies, or evaluating cloud security risks.
Microsoft regularly updates Microsoft 365 capabilities and security features. Organizations should periodically review their cloud environment and security practices to ensure they continue to align with current best practices and evolving business needs.
Final Thoughts
Microsoft 365 has transformed how healthcare organizations communicate, collaborate, and manage information.
With that transformation comes greater responsibility.
Protecting Microsoft 365 isn’t about enabling every available security feature, it’s about implementing the right combination of identity protection, governance, device security, collaboration controls, employee education, and continuous monitoring to support your organization’s unique needs..
The most resilient healthcare organizations understand that cloud security is an ongoing operational discipline.
By investing in strong governance, thoughtful configuration, workforce awareness, and continuous improvement, healthcare leaders can reduce cyber risk, strengthen operational resilience, and create a secure technology foundation that supports exceptional patient care today and as their organizations continue to grow.
Frequently Asked Questions About Microsoft 365 Security
Healthcare leaders often have practical questions about securing Microsoft 365 while supporting productivity, collaboration, and patient care. Below are answers to some of the questions we hear most often from physicians, practice administrators, compliance officers, and healthcare executives.
Is Microsoft 365 HIPAA Compliant?
Microsoft 365 provides security, privacy, and compliance capabilities that can help healthcare organizations meet their regulatory obligations.
However, Microsoft 365 is not automatically HIPAA compliant simply because it has been deployed.
Healthcare organizations remain responsible for:
- Configuring security appropriately
- Managing user access
- Protecting patient information
- Developing organizational policies
- Training employees
- Monitoring security events
- Managing vendors
- Conducting Security Risk Assessments
HIPAA compliance depends on how technology is implemented, governed, and used, not simply which platform is selected.
Is Multi-Factor Authentication Really Necessary?
Yes.
Passwords alone are no longer sufficient to protect healthcare organizations from today’s cyber threats.
Multi-Factor Authentication (MFA) significantly reduces the likelihood that stolen credentials alone can be used to access organizational systems.
Because compromised Microsoft 365 accounts are frequently targeted by attackers, MFA should be considered a foundational security control.
Should Every Employee Have an MFA?
In most healthcare environments, yes.
Although implementation approaches may vary depending on operational needs, organizations should work toward enabling MFA for all users whenever practical.
This includes:
- Physicians
- Nurses
- Administrative staff
- Billing personnel
- Executives
- IT administrators
- Remote workers
Consistent adoption helps reduce organizational risk and simplifies security management.
How Often Should Microsoft 365 Security Be Reviewed?
Microsoft regularly introduces new capabilities, updates, and security enhancements.
Healthcare organizations should periodically review:
- Identity management
- Conditional Access policies
- Administrative permissions
- External sharing
- Security alerts
- Collaboration settings
- Workforce awareness
- Device management
Regular reviews help ensure that security practices continue to align with organizational growth and evolving cybersecurity risks.
Are Microsoft Teams and SharePoint Secure Enough for Healthcare?
Microsoft Teams and SharePoint offer robust security capabilities.
However, security depends on how they are configured and governed.
Organizations should establish policies addressing:
- Guest access
- External collaboration
- File permissions
- Information sharing
- Data retention
- User responsibilities
Technology should support secure collaboration, not replace governance.
Can Employees Use Personal Devices to Access Microsoft 365?
Many healthcare organizations support Bring Your Own Device (BYOD) programs.
If personal devices are permitted, organizations should establish clear expectations regarding:
- Device security
- Screen lock requirements
- Encryption
- Remote wipe capabilities
- Approved applications
- Reporting lost or stolen devices
Policies should balance workforce flexibility with organizational security and patient privacy.
What Is the Biggest Microsoft 365 Security Mistake?
The most common mistake is assuming Microsoft manages every aspect of security.
In reality, healthcare organizations remain responsible for securing:
- Users
- Identities
- Permissions
- Devices
- Collaboration settings
- Data governance
- Organizational policies
Cloud technology changes how security is managed, but it does not eliminate the need for security management.
Leave a Comment